Home
»
Posts filed under
hacking
Showing posts with label hacking. Show all posts
Multiport Scanner [Python]
As network analysis or pentester , or maybe hacker you have been hear about Nmap port scanning .. A great tools for scanning process to find out what port / IP that live / open.
But how about "Multiport" ?
Multiport is a port scanning utility designed in Python. It accepts the target and ports (single port, port list and port range) as user input. Then scans the target for the port(s) status using the scanning techniques all at once. The output is displayed in an organized table format.
The function is same with Nmap but the output is more easy to readable because the script is using PrettyTable plugin and also you did'nt need to select which method scanning to use . Ex : Syn Scan , TCP Scan , XMAS Scan .
You can get the script from here . Multiport
If you get a error same like this . Follow the instruction to resolve it.
Go here and download newly PrettyTable plugin .
Or Just follow this step .
wget http://prettytable.googlecode.com/files/prettytable-0.7.2.tar.gz
tar -xzvf prettytable-0.7.2.tar.gz
cd prettytable-0.7.2
python setup.install
Ok's now multiport script will not be error . You can try it
This is my result when try scanning.
MAN IN THE MIDDLE ( MITM) ATTACK : USING WIRESHARK AND CAIN & ABEL
Today i got a request from my friend , he wants to know how to use wireshark and cain & abel tools. To make this tutorial interesting i will show how do MITM attack including ARP Cache Poisoning. Then we will inject the cookies we get , to browser for hijack the account.
You will get a list of IP depend on the client on the network. Make sure that you know which one is Client IP (Victim) and your Gateway IP ( Router ). For my case , 192.168.0.1 is my Gateway IP and 192.168.0.102 is Client IP.
After that , Click APR tab that has radioactive sign. then click on "+ " sign
First click on your Gateway IP ( 192.168.0.1) on the left option , and click Client IP ( 192.168.0.102) on right option.
Select Gateway IP and Start APR by click radioactive sign.
Run Wireshark tools.
Select the network interface that currently used by click Interface List. To confirm which interface is it , look at the packet. In my case WiFi is my currently network interface used , tick on it and Start.
You will get a lot of data. To confirm that you ARP Cache Poisoning is succesfull look at the Source , it will listing the Victim IP.
To steal the cookies of victim , Filters the result with "http.cookies" .
Then click on Hypertext Transfer Protocol , identify where is cookies from "www.blogger.com" , and copy truncated cookies.
To inject cookies on your browser you will need a Tampermonkey extenison (Chrome user) or Greasemonkey extension (Firefox user ). Download Tampermonkey here Greasemonkey here.
And also Cookie Injecter script here.
Restart Your Browser. Goto to website that the cookies come from. In my case is "www.blogger.com"
Press ALT + C button to get the injector cookies pop up.
Paste The cookies on the fill box. Then refresh the browser.
Now you have access to the blogger page admin without need to know the username and password. Cookies can be used untill the victim did not logout the account.
Oftenly this technic is used by Hacker on CyberCafe , school network , Wifi Hotspot to steal facebook cookies.
CLICK HERE TO KNOW ABOUT MITM ATTACK.
Please make sure that this two tool has been installed on your machine. You can get Wireshark here , Cain & Abel here. If your antivirus keep annoy about this tool just ignore. Sometime when you run Cain & Abel the popup say WinPcap driver not found please install it first , you can get it here
Lets start the tutorial. On your Cain & Abel , Click on Sniffer tab , active the sniffer and click "+" sign.
Check on All hosts in my subnet and tick on All Tests for more .
You will get a list of IP depend on the client on the network. Make sure that you know which one is Client IP (Victim) and your Gateway IP ( Router ). For my case , 192.168.0.1 is my Gateway IP and 192.168.0.102 is Client IP.
After that , Click APR tab that has radioactive sign. then click on "+ " sign
First click on your Gateway IP ( 192.168.0.1) on the left option , and click Client IP ( 192.168.0.102) on right option.
Select Gateway IP and Start APR by click radioactive sign.
Run Wireshark tools.
Select the network interface that currently used by click Interface List. To confirm which interface is it , look at the packet. In my case WiFi is my currently network interface used , tick on it and Start.
You will get a lot of data. To confirm that you ARP Cache Poisoning is succesfull look at the Source , it will listing the Victim IP.
To steal the cookies of victim , Filters the result with "http.cookies" .
Then click on Hypertext Transfer Protocol , identify where is cookies from "www.blogger.com" , and copy truncated cookies.
To inject cookies on your browser you will need a Tampermonkey extenison (Chrome user) or Greasemonkey extension (Firefox user ). Download Tampermonkey here Greasemonkey here.
And also Cookie Injecter script here.
Restart Your Browser. Goto to website that the cookies come from. In my case is "www.blogger.com"
Paste The cookies on the fill box. Then refresh the browser.
Now you have access to the blogger page admin without need to know the username and password. Cookies can be used untill the victim did not logout the account.
Oftenly this technic is used by Hacker on CyberCafe , school network , Wifi Hotspot to steal facebook cookies.
CLICK HERE TO KNOW ABOUT MITM ATTACK.
IMPORT CONTACT FB VIA YAHOO.MAIL
Today i will show , how to import email contact form your facebook to yahoo mail. This is also once of technic Information Gathering.
To make this tutorial work , what do you need is a Yahoo.Mail accounts , and a Facebook account either using a Gmail.Mail or Yahoo.Mail ( i had try two of this and its work ).
First , login to Yahoo.Mail and Facebook account. Then on your Yahoo.Mail checkout the CONTACTS tab. Click symbol " + " on LISTS to make a new folder.
Then click on import Contacts . Select Facebook.
And you done with it.
Information Gathering Using Social Network
Information Gathering or IG is a process to collecting data of someone "victim" , to make preparation before we attack the victim. With IG we can find what the vulnerabilities that has on the victim.
For this tutorial i will show how usually i do this technic on social network , and this tutorial i will show how to search their names , email address , fon numbers , recovery email address , their website.
FOR EDUCATIONAL PURPOSE ONLY (For some reasons this tutorial will be picture only)
CASE 1 :

CASE 2 :
How to Use Whois in windows
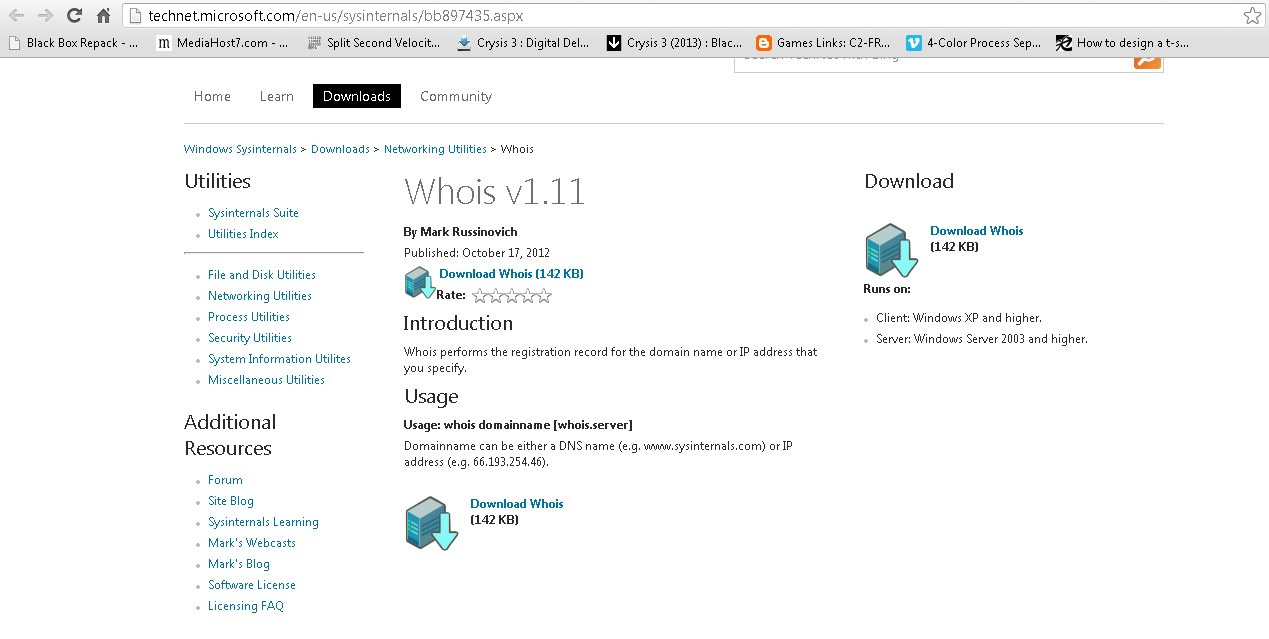
Whois is a tool to performs the registration record for the domain name or IP address that you specify. And by default its preinstalled on linux and *unix operating system. Unfortunatelly for windows user you have to installed it manually.
Usually the penetrate system using this whois to collecting data or it called reconnaissance phase. Whois also can be performed on web based , Ex whois.net
This tutorial i will show , how to performed whois on windows machine. Get whois from technet microsoft
Extract zip file on C:\ directory
Open up command prompt goto whois folder

type in whois.exe and you will prompt with a popup , click on accepted

Usage is : whois [-v] domainname [whois.server]
And you will get a lot of detail of the registrar. Please note , use this skill for learning only dont do this for a hacking.
Usually the penetrate system using this whois to collecting data or it called reconnaissance phase. Whois also can be performed on web based , Ex whois.net
This tutorial i will show , how to performed whois on windows machine. Get whois from technet microsoft
Extract zip file on C:\ directory
Open up command prompt goto whois folder
type in whois.exe and you will prompt with a popup , click on accepted
Usage is : whois [-v] domainname [whois.server]
- [ ] : is a optional
- domainname either web site address or their ip address
- whois.server is name of registrar that the domain has been registered.
And you will get a lot of detail of the registrar. Please note , use this skill for learning only dont do this for a hacking.
Test Your Password Strength
Because i'm likely using Bruting Force technic to guessing victim password..I search a site that will check the strength of a password and i found https://howsecureismypassword.net/
This site will check the password strength and give a estimate time to crack it. Im trying a keyword [PleaseGiveMe_Password] and it give a 2 octillion years to crack it :)..
Man In The Middle Attack (MITM)
The man-in-the-middle are attacking technic that intercept communication between two system or computer. So that we can sniff all the data that being request by the victims. The data that request by the victims also can be modify or read.
This technic only work when you are in same network with the victims. Like wifi connection, cc, school lab, and others.
This diagram shows us a normal communication wlan
This diagram shows us how the-man-in-middle-attack work
This technic only work when you are in same network with the victims. Like wifi connection, cc, school lab, and others.
This diagram shows us a normal communication wlan
So from above diagram, we can see that the attacker PC was locate at the middle between the victim A and victim B. That means all the request from victim A and B are through attacker PC. Attacker PC can read the request of victim also edit the request.
Real Situation (Educational Purpose Only)
For this tutorial i will use :
- Windows 7 as victim
- Bactrack 5r3 Linux as attacker (running in virtual box)
- Ettercap - already installed in Backtrack
Step :
1. Launch Backtrack
2. Launch Ettercap-GTK
3. Choose unified sniffing
4. Choose Network Interface (in my case eth0)
5. Scan for hosts
6. Click host list
7.Choose modem IP as add to target 1 and victim IP as add to target 2. You can select more than 1 IP for victim but makesure it's not your IP :)
8. Click MITM > ARP Poisoning > Sniff Remote Connection
9. Start Sniffing
For this tutorial i will show how to sniff HTTP (Not HTTPS) login name and password
10. Victim try to login HTTP page